Business security improves when routine decisions happen consistently, records stay current, and teams receive warnings before a small issue grows. Automation supports those outcomes by connecting identity data, building systems and operational workflows.
It can approve standard requests, remove expired permissions and create reliable audit records without requiring an employee to complete every task manually. Used carefully, these systems give security teams more time to investigate unusual activity and improve policies.
The Rise of Smart Workflows
Smart workflows connect events to predefined actions. If an employee reports a lost badge, for example, an automated process can disable it, notify the appropriate team and open an incident record within seconds. No one has to copy the same information between separate systems.
Effective automation should support business priorities. Guidance on security automation strategy recommends aligning automated processes with organizational goals and existing risk controls. Start with a workflow that has clear triggers, predictable decisions and measurable results. Track processing time, missed alerts and manual interventions so you can see whether the workflow is producing a real improvement.
Automating Access Management
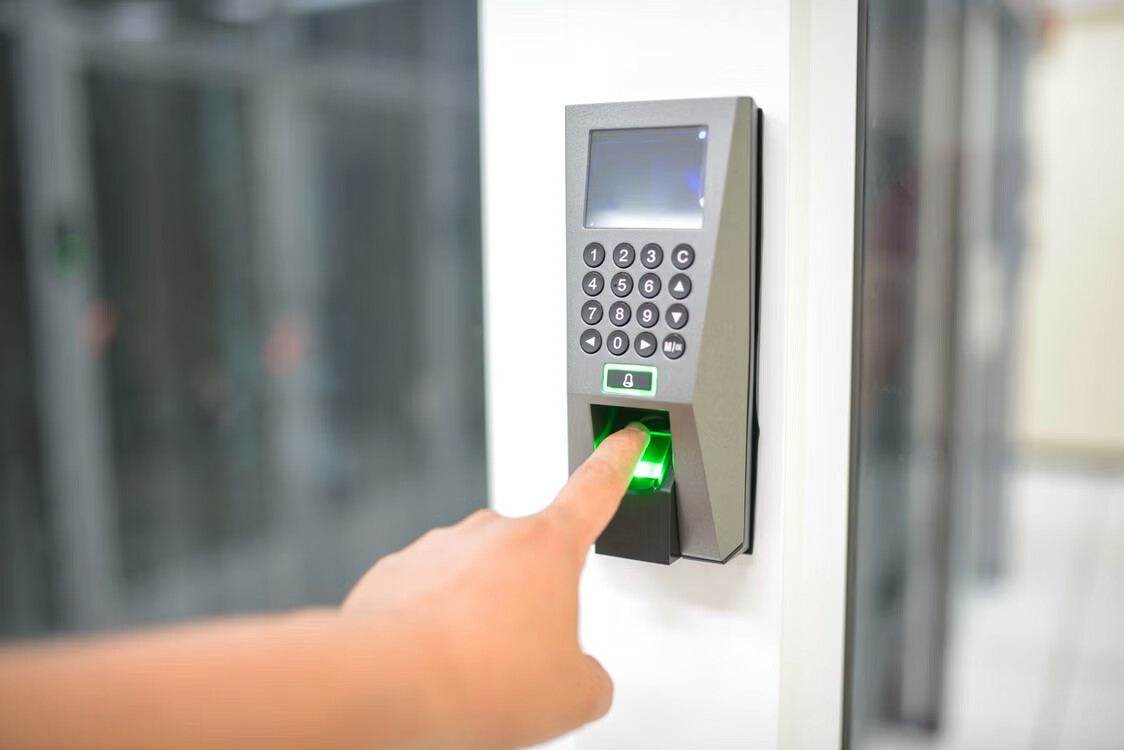
Employee arrivals, role changes, and departures create frequent permission updates. Delays can prevent new hires from entering approved areas or leave former staff with permissions they no longer need. Connecting human resources records with access control helps enterprises manage these changes across multiple locations while improving monitoring, reporting, and incident response.
Set role-based rules before automating approvals. A facilities coordinator might need weekday entry to several offices, while a contractor could receive permission for one site during a defined two-week project. Managers should approve unusual requests and high-sensitivity areas. Detailed IAM automation practices also highlight automated provisioning, removal and periodic reviews as useful controls.
Saving Time and Resources
Manual security administration often involves email chains, spreadsheets and repeated data entry. A simple request may pass through a manager, facilities staff and an IT administrator before anyone completes it. Automation can route the request, verify required approvals and record each action in one workflow.
Measure the current process before selecting software. Record how many requests arrive each month, how long each type takes and where work tends to stall. A workflow handling 500 routine requests per month saves substantial staff time even if each automated transaction removes only five minutes of administration. Teams can then focus on exceptions, system maintenance and investigations that require context and judgment.
For businesses connecting automation across several departments, this guide to scaling AI workflows offers useful planning principles for integration and governance.
Reducing Human Error Risks
Repetitive tasks invite mistakes, especially when teams work across multiple applications. An administrator may mistype an employee number, overlook an expiration date or assign permissions based on an outdated job title. Automated validation can compare each request with current identity records and flag missing or conflicting details before approval.
Build safeguards into every workflow. Require a second review for sensitive permissions, limit automatic approvals to established roles and send alerts when a rule produces an unusual volume of changes. Keep a clear path for employees to report errors.
Automation also needs supervision. Review exception logs weekly during the first few months and test rules after organizational changes. A workflow built around last year’s department structure may produce incorrect outcomes after a merger or office reorganization.
Process Automation for Compliance
Compliance work depends on evidence. Auditors may ask who approved a permission, when it became active and whether the organization reviewed it on schedule. Automated workflows can timestamp each action, preserve approval records and generate recurring review tasks. That creates a consistent audit trail without requiring teams to reconstruct events from old messages.
Define retention periods, review schedules and ownership before activating the process. Reports should show completed actions as well as exceptions, failed integrations and overdue approvals. Limit access to compliance records based on job responsibilities and document any manual override with a reason.
Begin with one process that creates frequent administrative work, such as quarterly permission reviews or contractor expiration dates. A narrow pilot will reveal weak rules and missing data while the impact remains manageable. Once the results are accurate, the same control pattern can support other sites and departments.